


In Brief: The EU Digital Identity Wallet will let people present verified identity data and other credentials to public and private services across the EU. Businesses accepting it need to validate that evidence and connect the results to their existing onboarding, compliance, and risk decisions.
Document and biometric verification remain relevant for other identification routes and for enrollment, recovery, or additional checks where the approved process calls for them.
Denmark’s AltID already lets people present identity and age proofs within the country. Finland, meanwhile, plans to release its digital identity wallet in 2027. National services and their readiness for EU-wide use are therefore progressing on different timetables.
Businesses preparing to accept EUDI Wallets need to understand which customers can use them, which credentials their services need, and how verified information will enter their existing processes.
In this article, we explain which services must accept EUDI Wallets, how national projects are progressing, and what wallet verification involves. We also look at where document and biometric checks fit and how Regula’s technology can support national wallet projects.
Get posts like this in your inbox with the bi-weekly Regula Blog Digest!
What is the EU Digital Identity Wallet?
The EU Digital Identity Wallet lets people identify themselves and share verified information with public and private services, online and in person. Typically accessed through a smartphone app, each wallet is provided by, on behalf of, or with the recognition of an EU Member State under the revised eIDAS framework.
Its core identity credential contains person identification data (PID), issued by a trusted provider responsible for verifying the holder’s identity. Other organizations can issue credentials within their areas of responsibility, such as a university issuing a diploma or a licensing authority issuing a mobile driver’s license. The wallet gives the holder a way to receive, store, and present this information.
Services requesting information from the wallet are known as relying parties. These include government portals, banks, telecom operators, and car rental companies. The user can review and approve a request, and selective disclosure allows them to share particular attributes from a credential. Alongside identification and credential sharing, the wallet also enables users to sign documents with qualified electronic signatures.
What the wallet can carry

What the wallet can carry and support
An EUDI Wallet can hold identity data and other digital credentials for use across public and private services. The credentials people can obtain, and where they can use them, depend on national rollout and the organizations issuing and accepting them.
-
Digital identity credential (PID): Person identification data that allows the holder to identify themselves to public and private services
-
Mobile driver’s license (mDL): A digital credential showing driving entitlements, including vehicle categories and applicable restrictions
-
Access to public and private portals: Wallet-based identification and authentication for government portals, banks, and other participating services
-
Access to ePrescriptions: A Health ID credential that allows a pharmacy to identify the patient and retrieve their prescription from the connected healthcare system
-
Academic degrees and other qualifications: Diplomas, enrollment certificates, and evidence of professional qualifications
-
Social security documents: Digital credentials such as the European Health Insurance Card (EHIC) and PD A1 certificates confirming which country’s social security legislation applies
-
Other attributes: Verified information such as bank account details, including IBANs, or proof of a professional role
Travel-related uses, including digital travel credentials and boarding passes, have also been tested in EU wallet pilots. EWC explored these applications during its 2023–2025 project.
Which businesses must accept EUDI Wallets, and when?
Article 5f of the revised eIDAS Regulation establishes separate acceptance rules for public bodies, certain private services, and very large online platforms. Applicability depends on the service and its authentication requirements.
-
Public online services must accept compliant wallets where a Member State requires electronic identification and authentication for access.
-
Covered private services must accept them at the user’s voluntary request where EU or national law, or a contractual obligation, requires strong user authentication for online identification.
-
Very large online platforms designated under the Digital Services Act must accept and facilitate wallet authentication at the user’s request where they require authentication for access, using the minimum necessary data.
Member States have 24 months from the entry into force of the relevant implementing acts to provide wallets, corresponding to the end of 2026.
Covered private relying parties have 36 months, corresponding to the end of 2027.
Public-service and platform acceptance sit in separate provisions, so that the private-sector timetable applies within its specific scope.
WORTH NOTING | EUDI for regular citizens
For individuals, wallet use will remain voluntary. That’s why regulated businesses that need to verify their customers will not only need to accept EUDI, but also continue serving people through other identification methods.
How does EUDI Wallet verification work?
During an EUDI exchange, the wallet checks which business is requesting information and shows the customer what has been requested. Once the customer approves, it returns the selected attributes and associated proofs. That response, known as a presentation, is what the receiving service validates.
The verification component checks four related properties:
-
Issuer trust: The verifier checks that the organization issuing the credential is recognized for that credential under the applicable trust framework.
-
Authenticity and integrity: The verifier validates the issuer’s digital signature and confirms that the disclosed information matches what was signed.
-
Validity and status: Expiration and the applicable suspension or revocation checks establish whether the credential, issuer, and wallet can still be relied on.
-
Connection to the wallet and request: Required cryptographic proofs link the presentation to the wallet and this particular exchange, helping prevent reuse in another session.
The wallet also authenticates its user before allowing a presentation. Where the relying party trusts the certified wallet’s mechanisms and verifies the required binding, this can provide assurance that the presenter is the person entitled to use the credential. A permitted additional holder check may provide further assurance where the use case calls for it.
After validation, the attributes enter the business’s own onboarding or service decision. Linking them to an existing customer record and completing any other required due-diligence checks remain part of that process.
How is EUDI progressing across Europe?
Several EU states already had very mature national digital ID systems before EUDI came along, and those systems are now being extended or coupled to wallet projects. Let’s take a look at some of the most advanced ones.
National apps already in use
Denmark’s MitID supports sign-in to public and private services through an app or alternative hardware. AltID, a separate app launched in June 2026, provides identity and age proofs for domestic use, with EU-wide use planned.
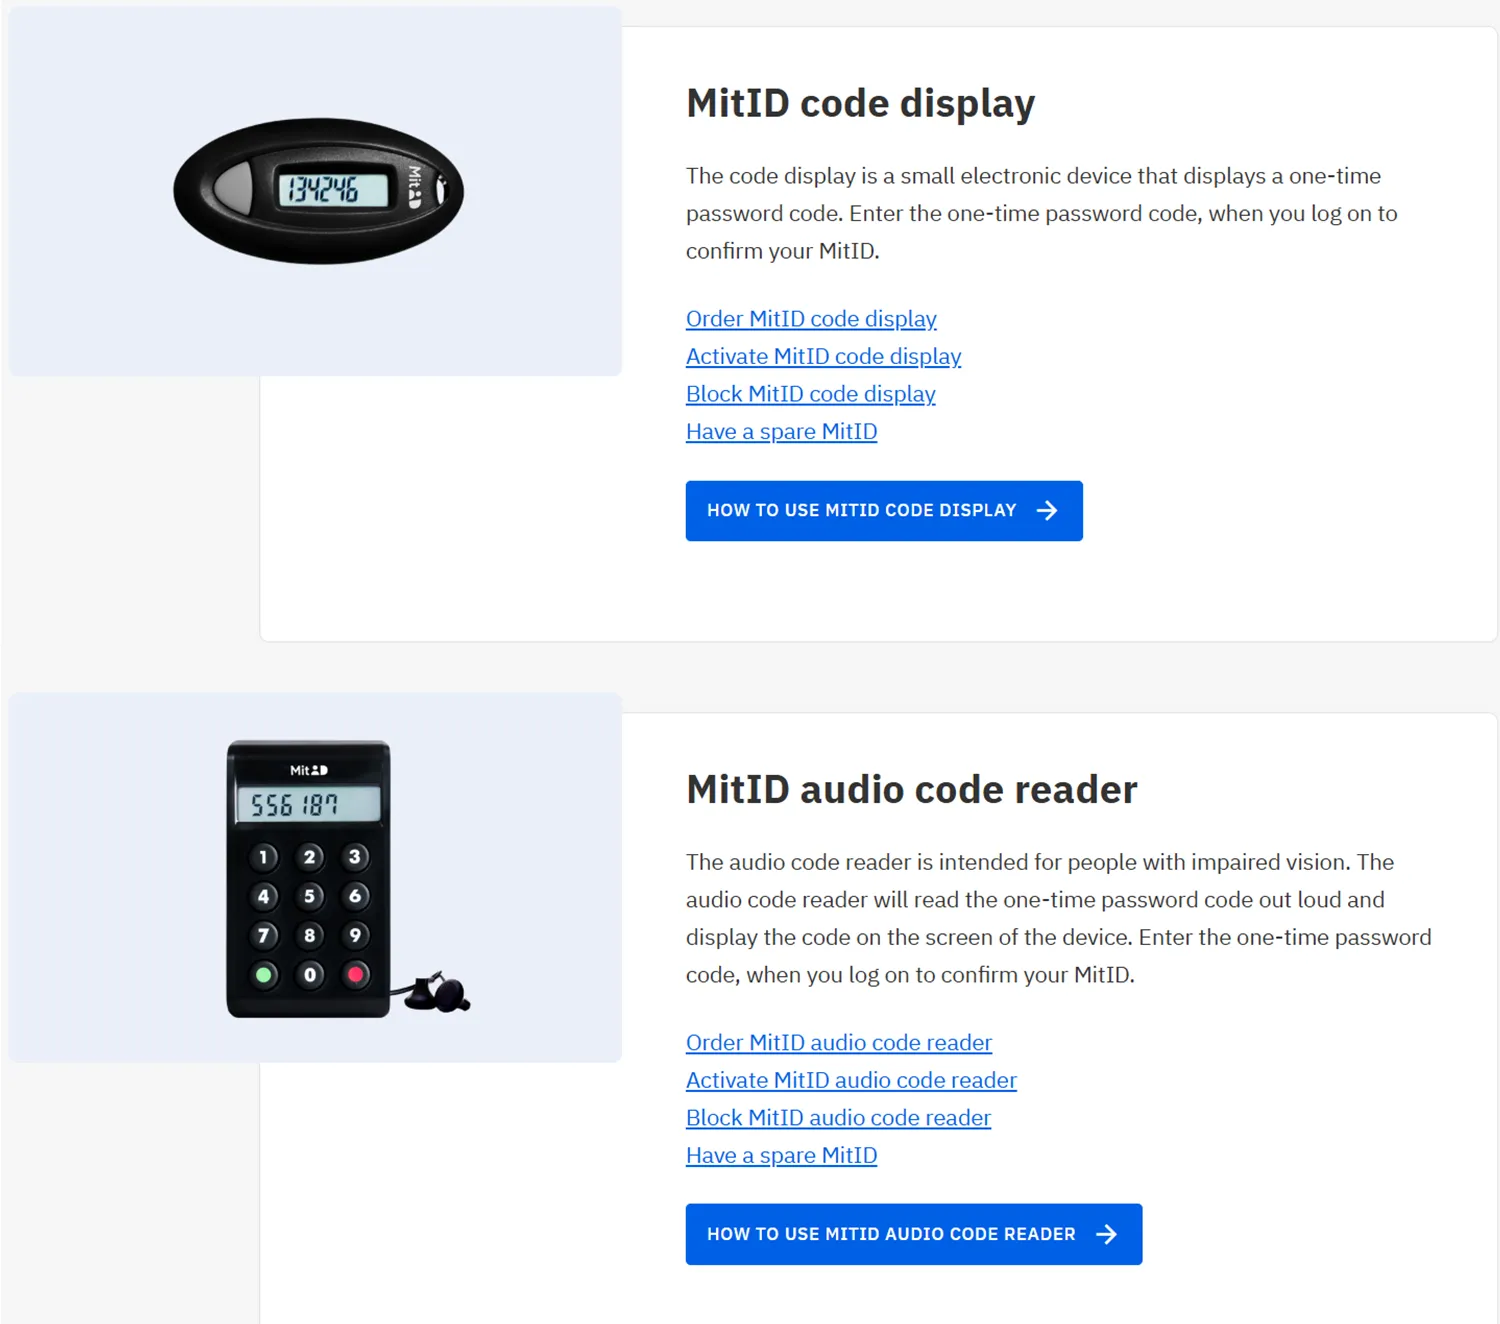
Interestingly, the app can be supplemented by a number of simple yet robust hardware devices, meant for various target groups.
Poland’s mObywatel already provides national digital documents. Its EUDI Wallet capability is being developed within the same ecosystem, with a pilot version planned for December 2026.
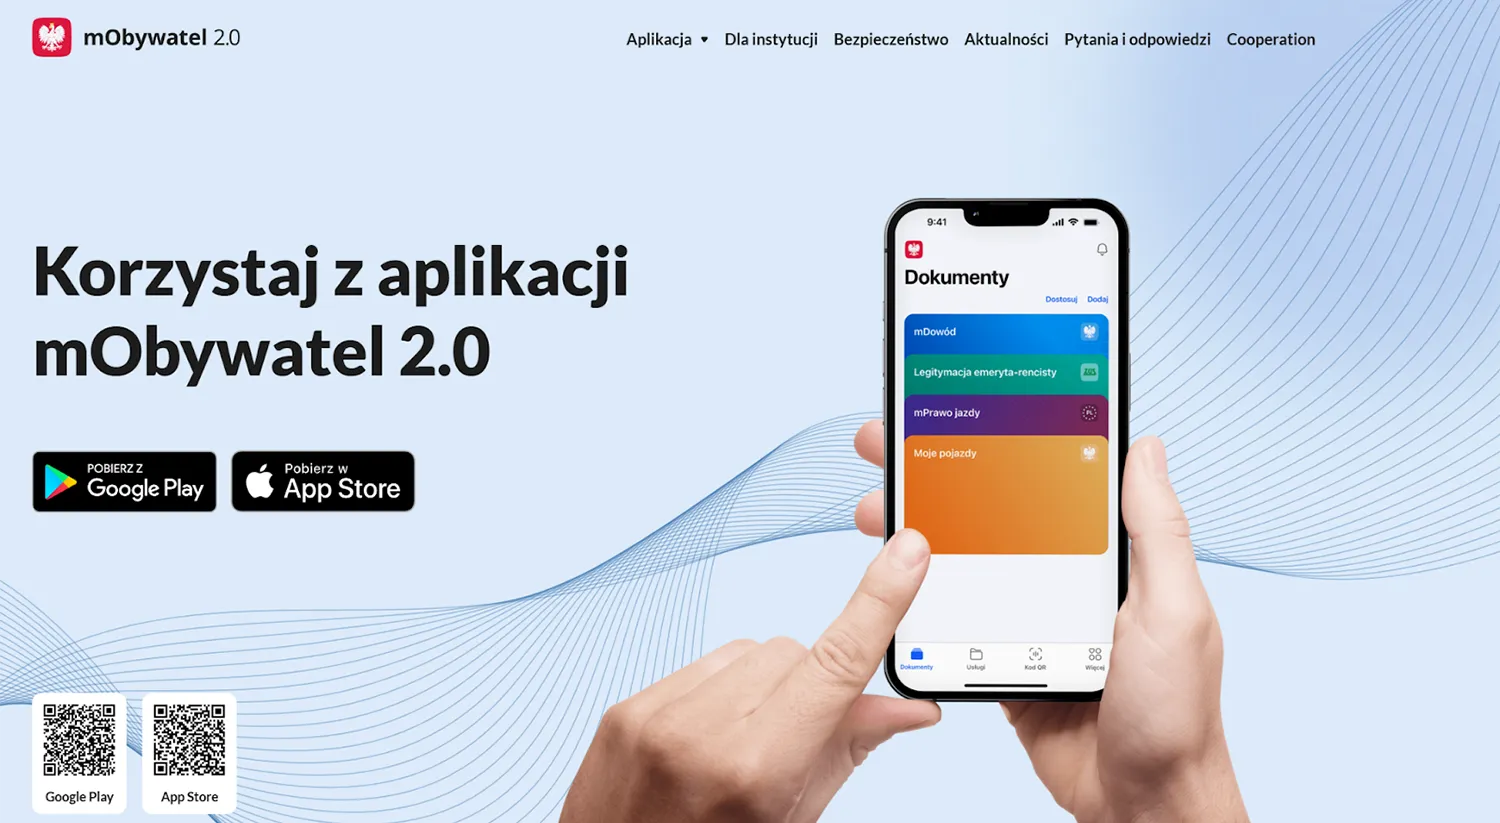
It is expected to add cross-border use inside the EU and free qualified signatures, while keeping the app familiar for existing users.
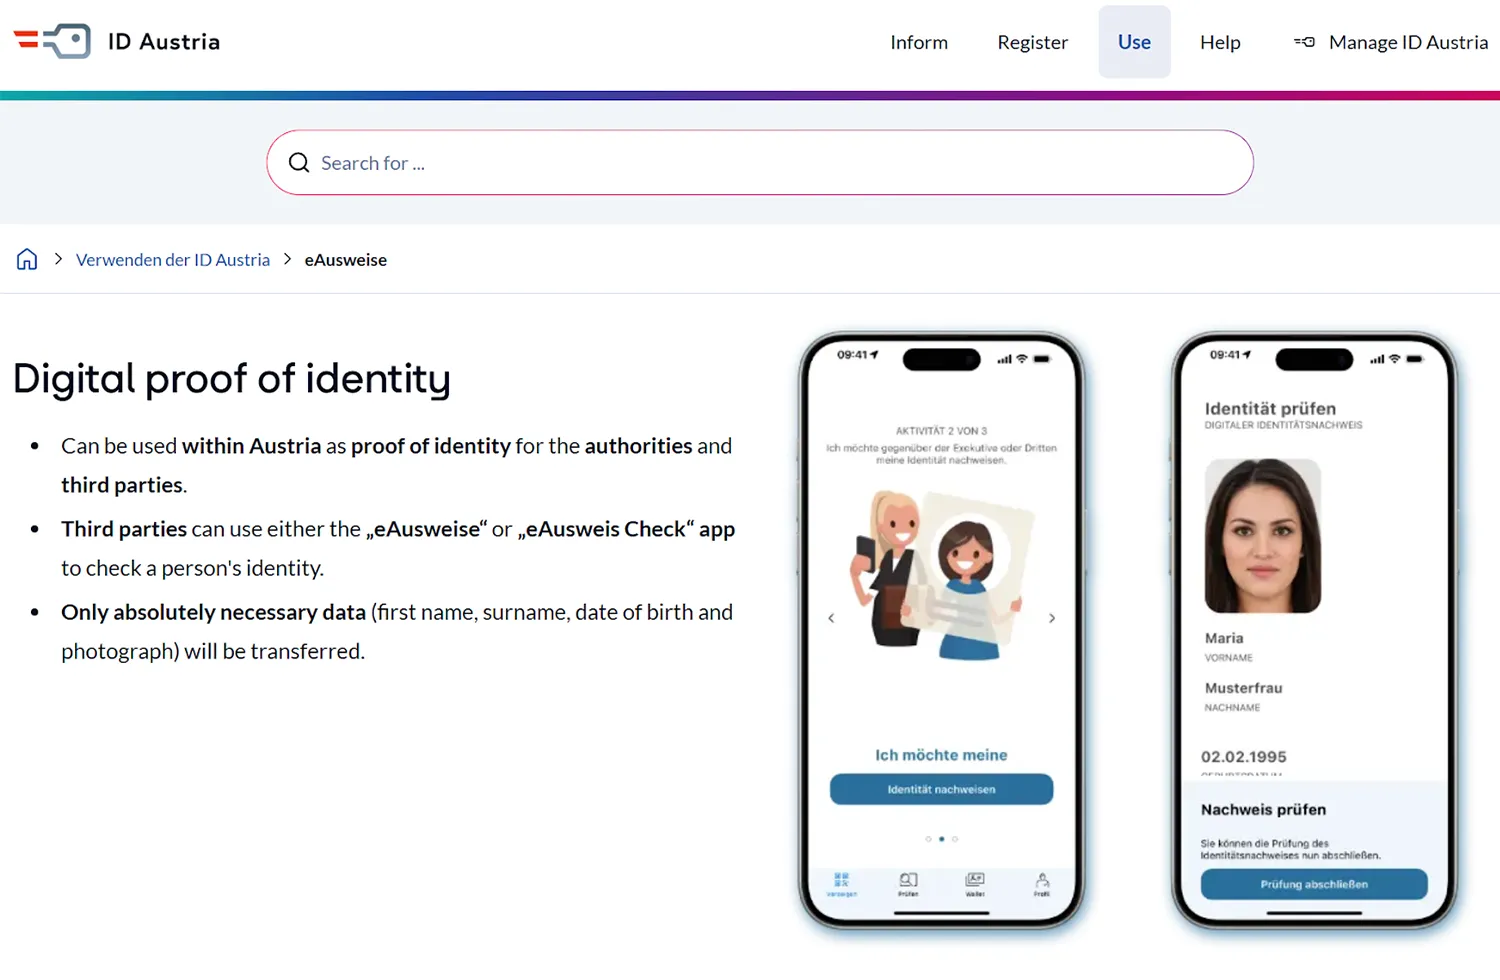
In Austria, ID Austria handles online identification, and eAusweise lets people present digital documents, including a driver’s license and proof of age, within the country.
Belgium combines the itsme identity service with the government’s MyGov.be app, which stores official documents and messages. MyGov.be can be activated using itsme or an eID card and is being developed toward its EUDI role.
Testing and preparations for launch
Germany provides a sandbox where companies and public authorities can test PID exchanges before d-you’s planned launch on January 2, 2027. Completing a sandbox test run will also remain an entry requirement for relying parties and issuers joining the German ecosystem.
Meanwhile, France Identité’s Playground is also open to service providers outside the original POTENTIAL consortium, making interoperability testing available to a wider group of organizations. Ireland is following a controlled pilot, with a wider public release planned for 2026. These environments differ in who can participate and what they can test.
Some national schedules extend beyond 2026
Finland now places the release and certification of Suomi.fi-lompakko in 2027. Romania plans a public RO Wallet launch on January 14, 2027, after testing and a restricted beta scheduled for late 2026.
Sweden also has a longer development schedule. Digg plans a test-platform version for December 2026, a wider release in 2027, and a certified EUDI Wallet in 2029.
These national plans leave the EU deadline unchanged. Acceptance planning also needs to account for wallets issued elsewhere in Europe, alongside the availability of the local national wallet.
Where do document and biometric checks still fit?
A suitable wallet presentation supplies identity evidence that a customer would otherwise provide through a document-based process. Whether it is sufficient depends on the attributes and assurance required for that service.
Customers may choose another identification method or lack a usable wallet or credential. Regula Document Reader SDK can authenticate their identity document and read its RFID chip where available. Regula Face SDK can compare the person’s face with the document portrait and perform a liveness check when that route calls for biometric verification.
The reason a wallet flow stops also affects what happens next:
-
A declined request or technical problem: An alternative identification method may allow the customer to continue.
-
Tampering or an untrusted issuer: The business’s fraud and review rules can carry forward into any subsequent attempt.
-
A valid presentation with an unresolved requirement: An additional check can address the specific information or assurance still needed.
Keeping completed wallet verification useful helps avoid repeating checks unnecessarily. A further document or biometric check can then address an identified gap, with its purpose and necessity established for that service.
There’s also identity proofing before credentials reach the wallet. Depending on the approved enrollment design, an issuer may rely on an existing electronic identity or other evidence meeting the required assurance level. Document and biometric verification contribute where that process uses a physical identity document and a comparison with its holder.
Recovery follows the wallet provider’s approved process too. Document and biometric checks may support it where restoring access or reissuing credentials requires the holder to establish their identity again.
What should businesses look for in an EUDI integration?
We think it helps to start with the evidence the service already needs, because that establishes what the wallet integration must deliver. Product, compliance, and engineering teams then assess the same proposed process.
An assessment should cover:
-
Role and registration: The applicable acceptance duty and relying-party registration in the Member State where the organization is established
-
Data requirements: The declared purposes and requested attributes, their connection to customer records, and processing and retention rules
-
Verification coverage: Named wallets, versions, credentials, formats, and presentation protocols, including use on the same device and across different devices
-
Operational responsibility: Which component performs trust, status, and binding checks, which results the business receives, and who maintains certificates and handles failures
How the business intends to use the information shapes what it needs to request from the wallet. The customer approves the sharing of those details, and the organization remains responsible for having a lawful basis to process them. Its retention and access rules also apply to information received through a wallet.
Once those requirements are clear, compatibility testing can follow the information through a complete customer interaction: from the wallet receiving a request to the verified details reaching the business’s system. This shows whether the particular wallet and credential work with the service’s actual requirements.
And where a provider handles verification, the service agreement can define which checks it performs and which results and records it returns. That gives the business the information it needs to investigate a rejected presentation or explain an onboarding decision later.
Where Regula’s verification tools fit
Regula fits into the EU Digital Identity Wallet (EUDI Wallet) ecosystem as an identity proofing, credential verification, and identity assurance technology provider. It provides the trusted verification infrastructure behind wallet issuance, recovery, and business adoption.
Our soultions contribute in two main areas:
-
Before credentials are issued: Verify that the person enrolling is who they claim to be, using authentic identity documents and biometrics.
-
When credentials are used: Help banks, telecoms, and other businesses verify digital identity credentials and combine them with additional fraud and identity checks when needed.
For national wallet projects, we can work with government agencies and their technology partners to combine Regula IDV Platform, document and biometric verification, and appropriate partner components. The project’s requirements will determine which components Regula provides and how they connect with the wallet and credential infrastructure.
Regula Document Reader SDK authenticates identity documents and reads their electronic chips where supported, while Regula Face SDK provides face matching and liveness detection.
Our solutions also support mobile driver’s licenses under ISO/IEC 18013-5 in supported mobile and desktop configurations. They can request selected attributes and check the issuer’s signature and data integrity.
PARTNERSHIPS | Connecting identity checks with digital credentials
Our partnership with Indicio brings together Regula’s document and biometric verification and Indicio’s technology for issuing, storing, and verifying digital credentials. The collaboration’s intended scope includes support for formats specified for EUDI Wallets.
Separately, Regula IDV Platform integrates with Microsoft Entra Verified ID for credential issuance and presentation workflows. Regula supplies identity verification results, and Microsoft’s service handles credential signing and cryptographic validation within the Microsoft Entra Verified ID ecosystem.
To discuss the verification and integration requirements of a national wallet project, contact our team.


.webp)
