
Regula’s experts predict that in 2027, businesses will face closer scrutiny of what an identity check actually establishes, whether that assurance survives across workflows, and when fresh evidence is needed. The pressure will come from automated attackers, more specific regulatory expectations, and new ways for people and AI agents to interact with services.
Our 2026 identity verification predictions: The reality check
Last year, we identified eight developments that could shape the future of identity verification. They have progressed at different speeds: some are already influencing everyday business decisions, while others depend on infrastructure, standards, or technical advances still taking shape.
Here, we revisit those predictions to assess what the evidence supports, what needs more time, and where our interpretation has changed.
| ✅ Already happening | 🔄 Taking shape | 🕒 A longer road | ❓ Ahead of the evidence |
|---|---|---|---|
|
Age assurance Age checks are becoming product requirements. UK age-checking duties for services allowing pornography and certain other harmful content took effect in July 2025. |
Identity orchestration Businesses want verification methods to work together across a process. KuppingerCole’s 2026 evaluation framework lists orchestration as a core criterion for assessing identity verification providers. |
Reusable identity Reusable digital credentials still need integration across services. The EU’s 2026 wallet program is testing whether wallets, credential issuers, and service providers can work together. |
Minds as credentials Reasoning ability alone cannot establish who someone is. NIST’s identity-proofing requirements call for evidence linking a person to their claimed identity, so this idea remains speculative. |
|
AI-assisted threats FinCEN has documented AI-generated documents used in fraud. Evidence that coordinated AI attacks can defeat entire verification workflows remains limited, so that broader prediction still needs support. |
AI governance AI regulation is taking shape. EU AI Act requirements, including transparency obligations, are taking effect in stages, with different duties following different implementation dates. |
Post-quantum readiness Quantum-resistant cryptography is advancing, but adoption takes time. Fraunhofer demonstrated passport protocols designed to withstand quantum threats, highlighting the challenge of protecting long-lived documents. |
Money with instructions We overstated the link to identity verification. The Bank of England distinguishes payments triggered by conditions from money with restrictions on how it can be spent. |
Recap of our 2026 predictions: what held up, what needs more time, and what needs rethinking.
These predictions have followed different paths, shaped by adoption, regulation and technical constraints. Our 2027 outlook draws on that experience, examining the forces behind each trend and the evidence supporting it.
Identity verification trends in 2027: The challenge lies between checks
In 2027, identity verification challenges extend beyond onboarding. The challenge is what happens between checks: how businesses detect a change in control, verify an agent’s authority, and decide when the evidence they collected is no longer enough.
1. The attacker has read the manual
Horizon: 2027
Identity verification providers publish API documentation, sample code, and integration guides to help developers connect their systems to other services. These materials explain how verification works, but the same details could also help someone looking for ways around its checks. In 2027, we expect more attempts to use this information to probe identity systems, as AI makes unfamiliar documentation easier to understand and apply.
An attacker could use AI to explore how an integration handles failed checks, recovery requests, and exceptions. They might discover, for example, that onboarding requires a biometric check, while a poorly protected recovery route offers another way in. That would give them a reason to target the surrounding process rather than the biometric technology itself.
The risk extends to payment services, account access, and AI agents — anywhere documentation explains how a system allows sensitive actions. A useful comparison is vulnerability disclosure: public information can help attackers identify exposed systems. Our forecast extends that concern to everyday technical guides, which AI could help attackers study for ways around the rules.
Confidence: Medium. The October 2026 PHP2Shell disclosure showed how seriously organizations take the risk of vulnerability details becoming public: Sansec warned of mass attacks within minutes of the patch release, while some operators took websites offline as a precaution. AI could help attackers use integration guides to identify weaknesses around sensitive operations. Evidence of this specific pattern in identity verification remains limited.
What changes for enterprises? Test sensitive workflows as if the attacker has read every public guide. Check that recovery routes, fallback options, and exceptions enforce the required controls, monitor automated attempts across the whole process, and be ready to assess exposure when relevant technical details become public.
2. Identity verification solutions buyers will scrutinize the whole verification process
Horizon: 2027–2028
Document authentication, face matching, and liveness detection can each perform well in tests. But strong individual checks do not guarantee a secure verification process. A required step might be skipped, or a fallback route might let a customer proceed with weaker checks.
We expect buyers to look more closely at how these components work together in their own deployment. A provider’s certification will prompt more specific questions:
- Which configurations and scenarios were assessed?
- Were fallback routes and exceptions included?
- Would changing the workflow put it outside the assessed scope?
Regulatory enforcement shows why implementation matters. In March 2026, South Korea’s Financial Intelligence Unit cited Bithumb for completing customer checks using unreadable or recaptured identity documents, allowing transactions before required checks were complete, and failing to retain required document copies. The case illustrates responsibility for operating the process; it does not establish a requirement for independent end-to-end certification.
Confidence: Medium. Standards such as ETSI TS 119 461 already set requirements for identity proofing processes. Our forecast is that these requirements will carry more weight in purchasing decisions, with more buyers seeking independent assessment of the complete process.
What changes for enterprises? Buyers will need to check how closely a provider’s assessed process matches the workflow they plan to use. That review should cover alternative routes, exception handling, and which later changes would require further assessment.
3. A face match will need evidence of how the image was captured
Horizon: Already underway; 2027
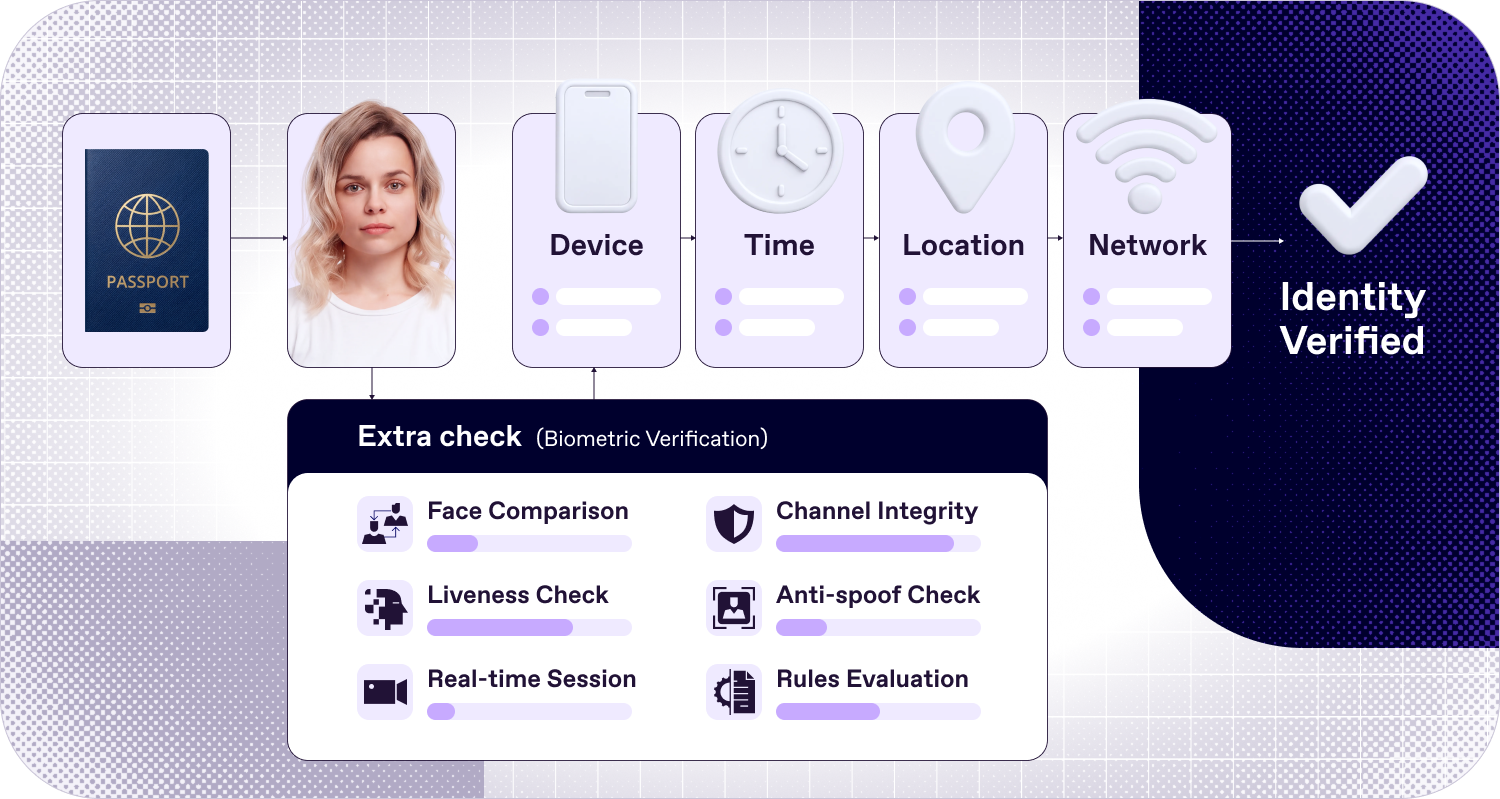
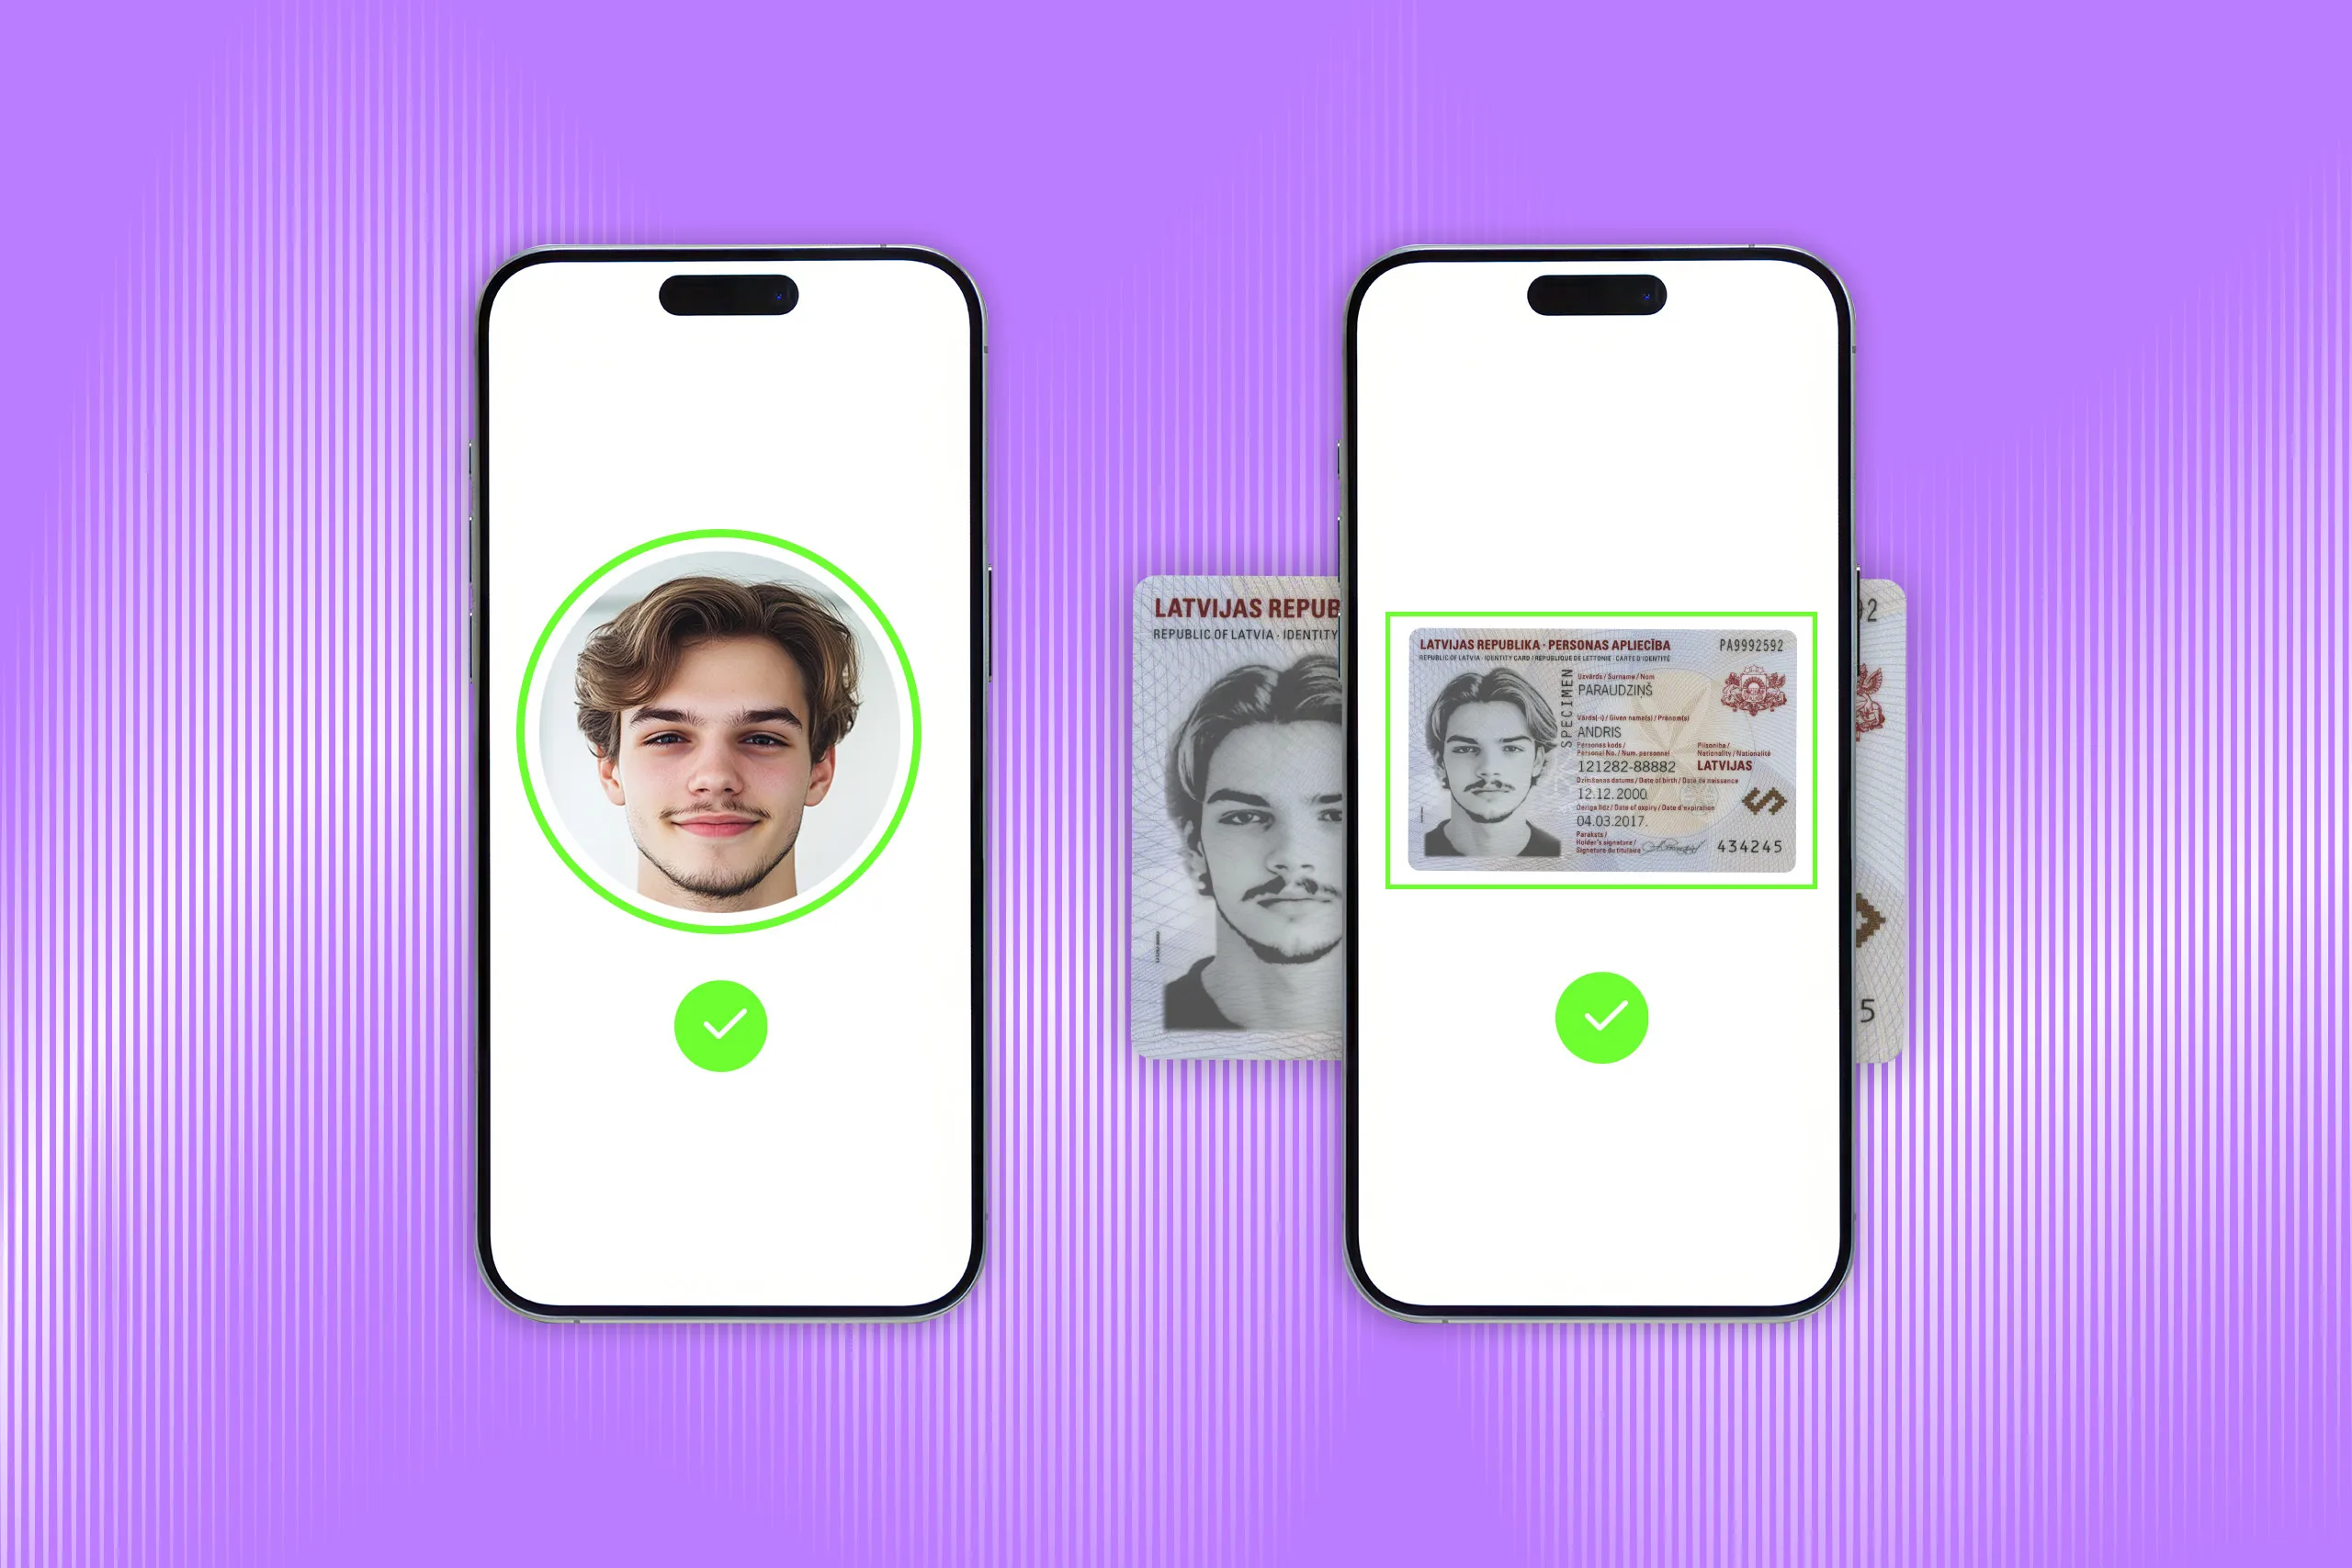
Scrutiny of the verification process also raises a more basic question: can the evidence entering it be trusted? Face matching technique measures how closely two faces resemble each other. Presentation attack detection looks for attempts to fool the capture system, such as presenting a photograph instead of a person. Neither check alone establishes where the submitted image came from or whether it was replaced after capture.
This is why capture provenance — the origin and handling of an image or video — will matter more. Providers will increasingly need to establish that evidence came from a genuine capture device during the current verification session and remained intact as it moved through the process.
Confidence: High. Regula’s 2026 global research report*, Identity Verification in the Age of AI Agents, found that 52% of businesses cannot fully verify that biometric data was captured live. At the same time, NIST SP 800-63A-4 requires controls to increase confidence that images and video come from genuine sensors during remote identity proofing, alongside checks for manipulation and protected data transmission.
What changes for enterprises? Businesses will increasingly assess how providers establish the origin of captured evidence, bind it to the capture device and verification session, and protect it against substitution. These safeguards will need to be evaluated alongside face-matching accuracy and liveness performance.
4. Businesses will need to explain how verification decisions were made
Horizon: Already underway; expanding in 2027
A customer passed verification six months ago. Now the account is under investigation, and the business needs to explain why that customer was approved:
- Which checks ran?
- Which rules and thresholds applied?
- Was an exception used, or did someone override the result? A “verified” status records the outcome but cannot explain how it was reached.
Answering these questions becomes harder when a decision involves several systems, data sources, and manual reviews. Businesses need a record that connects these contributions to the final outcome. That record must preserve what happened at the time, so investigators can reconstruct the decision even after the verification workflow has changed.
Confidence: High. Regula's 2026 research* found that 82% of organizations had been asked to explain an identity-related decision to a regulator, court, or external auditor. In a separate question, only 50% said they could fully reconstruct an identity verification decision. These findings show that demand for explanations already exceeds many organizations’ ability to provide them.
What changes for enterprises? Decision traceability will become a stronger requirement when choosing an identity verification platform, particularly in regulated industries. Buyers will need to assess whether the platform preserves the evidence, check results, rule and threshold versions, and any exceptions or overrides behind each decision — and keeps that history accessible after workflow updates.
5. The identity data you keep could become your next liability
Horizon: Already underway; accelerating in 2027–2029
Businesses will face closer scrutiny of the identity data they retain — and why they keep it. Legal obligations and investigations may require certain records to remain available. But retaining sensitive material also creates exposure: stolen document images or biometric data may help criminals impersonate customers. Each retention decision therefore needs a clear purpose, a defined period and appropriate access controls.
These decisions need to reflect the different purposes of the data. A document image, biometric template and verification log may be needed for different lengths of time.
Canada’s privacy regulator, for example, advises businesses to distinguish biometric information retention from that of associated personal information when their required retention periods differ. This allows businesses to preserve necessary records while deleting sensitive data they no longer need.
Confidence: High. Data minimization and storage limitation are already GDPR requirements, while anti-money laundering rules impose recordkeeping duties on covered businesses. We expect these obligations to make control over retained identity data a more prominent requirement in identity verification solution purchasing decisions.
What changes for enterprises? Buyers will increasingly assess how identity verification platforms manage retention, access, and data masking for different types of identity data. This includes whether teams can review verification results while personal details remain hidden, who can access the underlying evidence, and how deletion affects subsequent investigations and audits.
6. Fresh identity proof will be requested when the risk warrants it
Horizon: Already underway; accelerating in 2027–2028
A customer verified in January may not be the person controlling the account in May. A recovery request, an unfamiliar device, or a sensitive account change may warrant another check. The appropriate check depends on what the business needs to establish.
Reauthentication confirms that someone controls an authenticator linked to the account, such as a passkey or security key. Identity reverification checks whether that person matches the identity previously established. Account recovery can involve repeated identity proofing or other recovery methods, depending on the assurance required. A new device or recovery request therefore does not automatically require another document scan or biometric check.
Confidence: High. NIST SP 800-63B-4 already recognizes several account recovery methods, including repeating relevant parts of identity proofing. The forecast is that businesses will apply these distinctions more systematically when deciding which checks to request after onboarding.
What changes for enterprises? Businesses will need policies that define when existing evidence remains sufficient and which risks or events require additional checks. This will help them request fresh identity proof when needed while limiting unnecessary friction for legitimate users. Platforms will need to apply these policies, connect new evidence to the existing identity record, and repeat only the necessary verification steps.
7. Identity verification providers will need to show which official records they can check
Horizon: Already emerging; expanding in 2027–2029
A bank verifying a customer from another country may receive a passport that looks perfectly genuine. But was it actually issued? Is it still valid? And where can the bank check?
Many countries maintain official identity databases, but their responses may answer only part of the question. Some sources confirm that selected details match a record; others provide information about a document’s validity or status. Businesses need to understand that distinction before using the response in a verification decision. Matching details alone do not establish that the person presenting the document is its rightful holder.
We expect buyers to examine these differences more closely as providers bring official-source checks into their services. Providers can simplify access through fewer integrations, but they will also need to explain what each source covers and what its response actually confirms.
Confidence: Medium. AAMVA’s Driver’s License Data Verification service already supports real-time checks of submitted license and ID data against participating US issuing agencies. Wider international integration remains uncertain.
What changes for enterprises? Buyers will need to assess coverage by country and document type, confirm the provider’s authorized access, and understand the limits of each response. They will also need to define how source results contribute to a decision, along with document authentication and checks on the person presenting it.
8. Agent permissions will need to remain verifiable across services
Horizon: Already emerging; expanding in 2027–2029
A user authorizes an AI assistant to book a flight within an agreed budget. Completing that task may involve a booking platform, an airline’s system and a payment provider. Each service needs to verify that the agent has permission to perform the action it is being asked to do.
Permission recorded inside the assistant’s platform therefore needs to become evidence that other services can validate and interpret. We expect support for this exchange to expand across independent platforms, allowing an authorized task to proceed while preserving the user’s original limits.
The challenge is preserving the scope and validity of delegation across services with different access policies. Permission may expire, be withdrawn, or allow only limited delegation to another agent. Each receiving service needs enough evidence to decide whether to accept the request and to explain that decision later.
Confidence: Medium. The AP2 mandate for the Universal Commerce Protocol already specifies how authorization evidence moves between platforms, merchants, and payment systems. FIDO’s work on agent authentication and commerce provides a further route towards interoperability. These initiatives establish technical foundations; broader acceptance across independent services remains the forecast.
What changes for enterprises? Banks, merchants, and digital platforms must decide which delegation evidence they accept, whose authority they trust, and when they need fresh confirmation. The workflow must establish who can approve the change and connect that approval to the revised conditions. Existing identity evidence and authentication may be sufficient; stronger identity verification may be needed when there is uncertainty about who is granting or expanding permission.
9. Age assurance will become part of product design
Horizon: Already underway; expanding in 2027
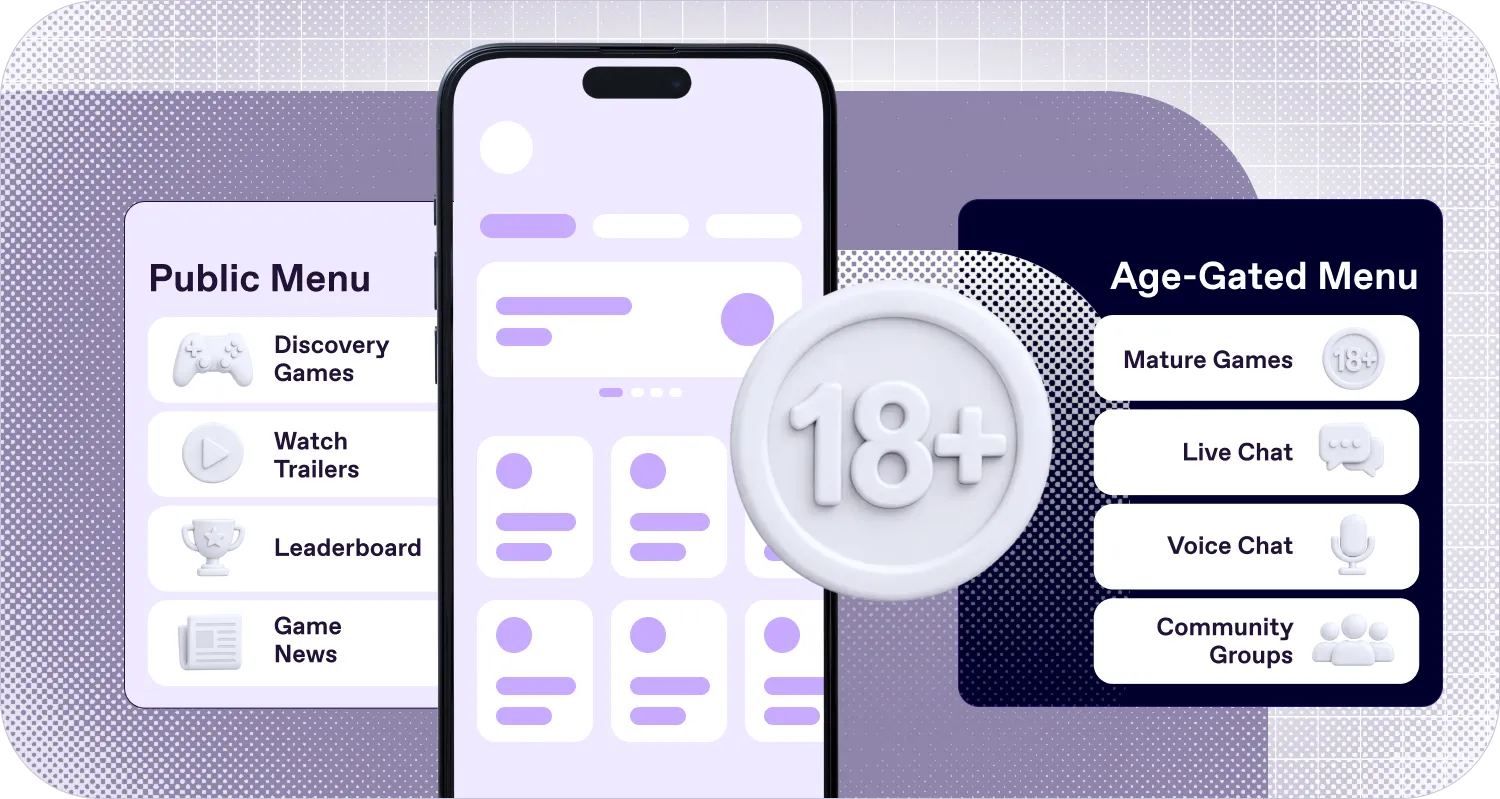
Age assurance will increasingly determine which content and features users can access. Platforms will need to decide where checks belong in the user journey and how to handle uncertain results.
A service may let users browse freely but require an age check to access a restricted feature. If an age estimate is too close to the required minimum to confirm eligibility, the product needs another verification route, with access withheld until sufficient proof is provided. Deciding when to check, what information to request, and how to resolve errors therefore becomes part of product design.
Privacy also shapes the design: a service may need only confirmation that someone meets an age threshold, without receiving their identity documents or biometric data.
Confidence: High. Roblox now requires age checks for chat access and restricts communication between age groups. Discord requests additional age assurance for certain content, spaces, and settings. These implementations demonstrate how age assurance already shapes product functionality.
What changes for enterprises? Digital platforms will need to redesign account access and feature permissions, integrate age checks at appropriate points, and support privacy-preserving verification — while minimizing compliance costs and user drop-off.
10. Data rules will shape where identity verification runs
Horizon: Already underway; 2027–2029
A global bank may use the same identity verification process in ten countries but face different rules for handling customer data. Some jurisdictions restrict cross-border transfers, while others impose specific requirements on biometric processing or data storage.
We expect these requirements to make deployment flexibility more important in procurement. Regional cloud, private cloud, and on-premises options may suit different needs. Businesses using several environments will also need coordinated policies, updates, and oversight.
Confidence: Medium. The GDPR’s international transfer rules and Saudi Arabia’s data transfer regulation illustrate the requirements multinational organizations must accommodate. Their influence on deployment decisions supports the forecast, although adoption of particular architectures will vary by market.
What changes for enterprises? Buyers will increasingly assess whether an identity verification provider’s deployment options and data flows meet their requirements, and how they can manage verification policies, updates, and oversight across regional environments.
Five questions enterprise leaders should ask their identity verification provider
Identity verification is becoming part of more business decisions. As requirements evolve, enterprises need to know whether their existing systems can support them without adding unnecessary complexity, costs, or risks.
1. Can someone bypass your strongest verification checks?
Strong document and biometric verification at onboarding means little if recovery or alternative workflows apply weaker controls. Enterprises need consistent protection across customer journeys throughout the identity lifecycle.
2. Can you verify the same customer again without starting from scratch?
A successful onboarding check cannot guarantee who controls an account months later. Identity assurance decays over time. Enterprises need to reconnect new evidence with previously verified identities and trigger reverification only when risk justifies it, without forcing customers through unnecessary repeat checks.
3. Could you explain a verification decision six months later?
A simple "verified" status offers little help during an investigation. Compliance teams need audit‑ready evidence, versioned decision logic, and full traceability so investigations can reconstruct what happened, why it happened, and who intervened.
4. Can you control where your identity data is processed and stored?
Different jurisdictions impose different requirements on sensitive identity data. Identity data, especially biometrics, must be processed where regulations require, without fragmenting verification standards across markets.
5. Can you introduce new verification requirements without rebuilding your system?
Verification requirements change constantly: new regulations, new evidence sources, new risk signals. Enterprises need workflows they can evolve without rebuilding their identity infrastructure every time the rules change.
How Regula Identity Verification Platform supports these requirements
1. Coordinate checks across connected customer journeys
The platform enforces consistent verification policies that run document authentication, face matching, liveness detection, geo, and additional checks for risk-based workflows configured by your team and further routes suspicious cases for manual review. Connecting onboarding, recovery, and support journeys to these workflows helps apply required verification steps consistently across different entry points.
2. Use identity history to support subsequent checks
The platform maintains persistent identity profiles connecting verification results and historical evidence across sessions, helping prevent weaker alternative workflows from becoming an easy path for fraudsters. This allows businesses to use previously collected evidence to inform subsequent checks, apply consistent verification policies, while managing data retention in line with their regulatory requirements, and avoid unnecessary actions without compromising security.
3. Keep verification records available for review
Regula IDV Platform maintains a history of verification sessions, checks, cases, results, and workflow actions. This gives auditors and compliance teams the evidence needed to trace verification decisions, review suspicious cases, and support audits.
4. Control the deployment environment
The platform supports on-premises and customer-managed cloud deployment, allowing businesses to process and store data within their own environment. Organizations can enforce their own access controls, network security policies, and data retention requirements and control the infrastructure where verification runs.
5. Adapt workflows as requirements change
Configurable workflows and third-party connectors let your team introduce additional checks and integrate external services. The platform coordinates these checks within the configured process, helping you accommodate new requirements without replacing the entire verification system.
.webp)